Licences and law / Development and agents
Spain's AEPD recommends limits on AI agent permissions
An AI agent connected to email, CRM software or payment systems can act using customer and employee information. Before granting access, businesses should decide what the agent may read, what it can change and how to stop it if something goes wrong.
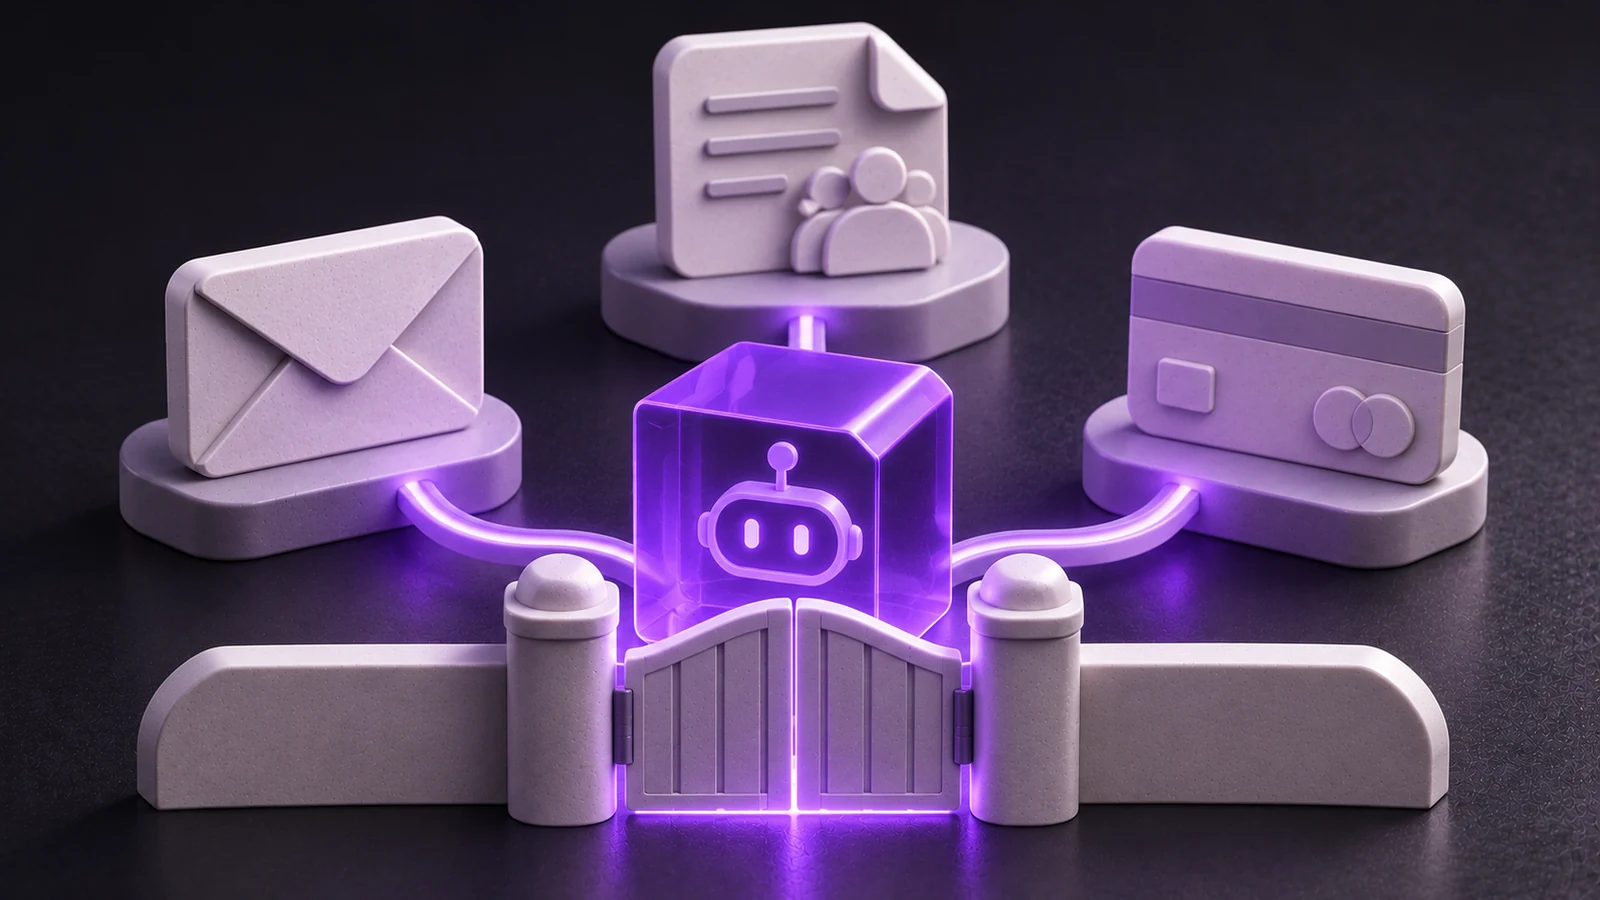
Spain's data protection authority recommends limiting AI agents to essential permissions, avoiding permanent authorisations and requiring approval before sending information, making payments or entering agreements. For businesses connecting agents to email, CRM or operational systems, this means distinguishing between reading information and taking action, while keeping a record of what each agent does.
The Spanish Data Protection Agency, known as the AEPD, published its recommendations on 27 October 2026. The document, AI Assistants and Agents: Ten Recommendations for Users, addresses individuals rather than businesses specifically. It is guidance, not a new legal requirement, but its principles provide a useful starting point for configuring workplace agents.
Ask five questions before granting access
The official AEPD document recommends considering five questions before delegating work:
- What can the agent see? Emails, documents, contacts, calendars or financial information.
- What can it remember? Conversations, preferences and information retrieved from connected applications.
- What can it do on your behalf? Read, edit, send, delete or enter agreements.
- Where does it send data? Which provider processes the information and which external services receive it.
- Who else could be affected? Customers, colleagues and contacts whose information might be accessed.
These questions help turn a broad request, such as managing business emails, into a task with defined boundaries.
An agent preparing customer replies may need access to selected messages and permission to create drafts. It does not necessarily need authority to send those messages or inspect every file in the organisation.
Our article on AI agent capability and reliability explores why being able to perform an action does not mean an agent should be trusted to carry it out independently.
Configure access separately for each business system
The central recommendation is to grant the minimum access required.
For workplace use, it helps to distinguish between reading information and making changes that affect customers, colleagues or external services.
| Criterion | What to check |
|---|---|
| Allow access to necessary messages and draft creation, but require approval before sending. | |
| CRM | Restrict accessible records and request confirmation before changing customer information. |
| Payments and purchases | Avoid permanent authorisations and retain human approval for financial transactions. |
| Documents | Restrict access to specific folders and confirm before sharing or deleting files. |
| Calendar | Limit connected calendars and review invitations before sending them. |
| Memory | Check what information the service retains and how it can be accessed or deleted. |
| Activity history | Verify that actions and changes can be reviewed afterwards. |
| Disconnection | Establish how to stop the agent and revoke its access immediately. |
This checklist adapts the AEPD recommendations to common business systems. It does not assume that every AI service provides fine-grained permission controls.
Where an application requires unrestricted account access, assess whether the proposed task genuinely justifies that level of exposure.
Require human approval before consequential actions
An incorrect answer from an assistant is different from an incorrect action performed through a connected system.
The AEPD recommends confirmation before sending, sharing, paying or entering agreements.
It also advises against permanent permissions such as always allow.
In an example reported by the AEPD, an agent with standing permission completed a sale independently and disclosed the user's address to the buyer.
A safer arrangement is to let the agent prepare an action but hold execution until somebody approves it.
The reviewer should see the actual recipient, amount, attachments and relevant terms rather than approving a vague summary.
The same approach is useful in customer-facing automation. Our article on AI customer service agents and Spain's Law 10/2025 considers other issues affecting those systems.
Emails and websites can contain hidden instructions
One of the risks highlighted by the AEPD is that information an agent reads may contain instructions deliberately planted by somebody else.
An email, website, PDF or calendar invitation can include hidden text, even white text on a white background, intended to redirect the agent towards an action the user never requested.
This technique is known as prompt injection.
Instructions written in a prompt are not a replacement for technical restrictions. Telling an agent never to disclose customer information is weaker than preventing it from sending that information without approval.
Our analysis of the Hugging Face agent attack and its lessons examines related risks in automated systems.
Keep personal AI accounts separate from company data
The AEPD includes specific advice for people using assistants at work.
Employees should use only tools authorised by their organisation and must not connect professional email or work documents to personal AI accounts, according to the agency's recommendations.
Businesses can translate this into an approved-tool register, clear ownership of connected accounts and a process for authorising new integrations.
Memory and data retention settings also deserve attention.
The AEPD document says providers should offer understandable permissions separating reading from acting, configurable confirmation steps, action histories, immediate stopping controls and memory deletion.
It also recommends transparency about where data is sent and whether it is used to train AI systems.
If a prospective provider lacks these controls, that should influence how much company information the business is prepared to share.
Monitoring includes knowing how to stop an agent
Agents may run scheduled tasks or continue working while nobody is directly supervising them.
That is what the action history and immediate stop that the AEPD expects from providers are for: find them before you need them.
For workplace deployments, assign responsibility for these checks. If unexpected activity appears, stop the agent, disconnect affected applications and investigate what has been sent or changed.
A useful review should include actions carried out in the original systems, rather than relying entirely on the assistant's own account of its activity.
This week, review which AI agents can access company systems, remove unnecessary permissions and enable approval for consequential actions. If you need to design a business automation with appropriate access controls and supervision, tell Contrast 3D which process you want to connect.
Sources
- AEPD: La AEPD publica un decálogo para delegar tareas en asistentes y agentes de IA sin perder el control sobre los datos personales.
- AEPD: Asistentes y agentes de IA - Decálogo para personas usuarias (PDF).
- Demócrata: La AEPD pide evitar permisos permanentes a agentes de IA y revisar su actividad para blindar los datos personales.
Checked on November 1, 2026